SAM I AM
27 September 2026
Summary
The attacker managed to gain Domain Admin on our rebels Domain Controller! Looks like they managed to log on with an account using WMI and dumped some files.
Can you reproduce how they got the Administrator's Password with the artifacts provided?
Place the Administrator Account's Password in DUCTF{}, e.g. DUCTF{password123!}
Analysis
We are provided with two backup files: sam.bak and system.bak. These are hives from an Active Directory machine and we will need them in order to retrieve the Administrator's password.
Windows fundamentals
Windows environments possess registry hives. They act as configuration files for when the operating system starts. Most registry hives are located in C:\Windows\System32\config. SAM and SYSTEM are two of the main registry hives:
- The SAM hive, short for "Security Account Manager", stores local credentials such as usernames, RIDs, LM hashes and NTLM hashes. Due to the sensitive information it contains, its content is encrypted with a key located in the SYSTEM hive.
- The SYSTEM hive stores important system information such as hardware, services and network information; this means we also need it in order to decrypt the SAM hive.
Solution
Dumping the SAM database
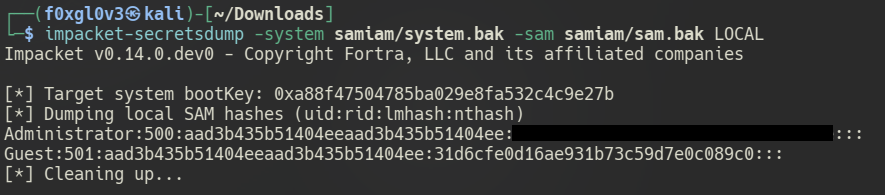
We are only interested by the last hash (NTLM hash). Let's save it to a text file:
echo -n '[REDACTED]' > admin_hash
Cracking the hash
My tool of choice is hashcat for password cracking. We will be doing a dictionary-based attack using the famous rockyou.txt dictionary:
hashcat -m 1000 admin_hash /usr/share/wordlists/rockyou.txt
-m 1000 -> Specify hash type, NTLM hashes are number 1000
It should take a few seconds to get the password. Make sure to submit it under the format specified in the summary.
Thank you for reading!
F0XGL0V3